


साइबर सुरक्षा एडभाइजरी
Summary
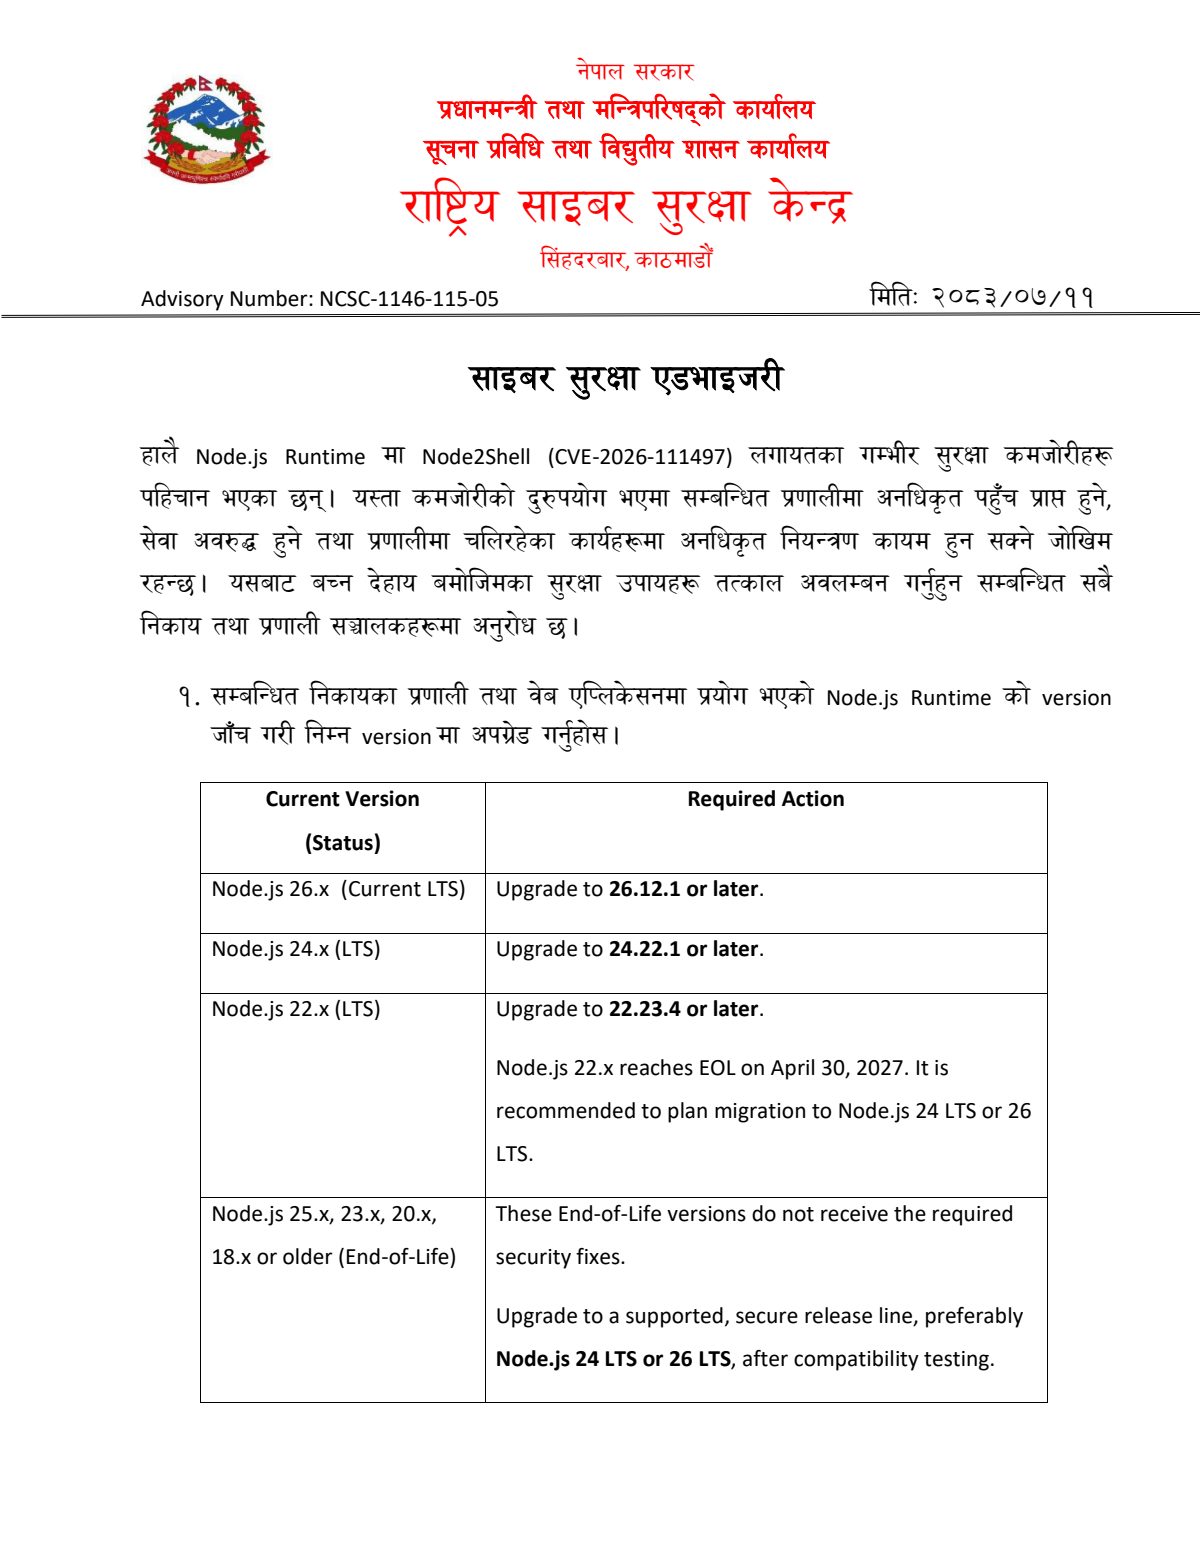
राविर् साइबर सरु क्षा के न्त्र धसिंहदरबार, काठमाडौँ साइबर सरु क्षा एडभाइजरी हालै Node.js Runtime मा Node2Shell (CVE-2026-111497) लगार्तका गम्भीर सरु क्षा कमजोरीहरू पवहचान भएका छन।् र्स्ता कमजोरीको दरुु पर्ोग भएमा सम्बन्त्न्त्धत प्रणालीमा अनधधकृ त पहुँचु प्राप्त हनु े, सेिा अिरुद्ध हनु े तथा…
Auto-generated and may contain errors. Check the original notice before you act on it.
Files
- b68caa32-7753-478f-9343-b7455dbe2ef6.pdfPDF · 3 pages · 293 KBOpen
Key details
- Organization
- National Cyber Security Center Singhadurbar , Kathmandu
- Industry
- Gov. Authority/Autonomo. Body
- Category
- Gen Info
- Published
- Notice date
- Fiscal year
- FY 2083/84
- Source
- View on the original website
Text extracted automatically from the notice (may contain errors)
नेपाल सरकार प्रधानमन्त्री तथा मन्त्न्त्रपररषद्को कार्ाला र् सूचना प्रविधध तथा विद्यतु ीर् शासन कार्ाला र् राविर् साइबर सरु क्षा के न्त्र धसिंहदरबार, काठमाडौँ Advisory Number: NCSC-1146-115-05 धमधत: २०८३/०७/११ साइबर सरु क्षा एडभाइजरी हालै Node.js Runtime मा Node2Shell (CVE-2026-111497) लगार्तका गम्भीर सरु क्षा कमजोरीहरू पवहचान भएका छन।् र्स्ता कमजोरीको दरुु पर्ोग भएमा सम्बन्त्न्त्धत प्रणालीमा अनधधकृ त पहुँचु प्राप्त हनु े, सेिा अिरुद्ध हनु े तथा प्रणालीमा चधलरहेका कार्हा रूमा अनधधकृ त धनर्न्त्रण कार्म हनु सक्ने जोन्त्िम रहन्त्छ। र्सबाट बच्न देहार् बमोन्त्जमका सरु क्षा उपार्हरू तत्काल अिलम्बन गनहाु नु सम्बन्त्न्त्धत सबै धनकार् तथा प्रणाली सञ्चालकहरूमा अनरु ोध छ। १. सम्बन्त्न्त्धत धनकार्का प्रणाली तथा िेब एन्त्ललके सनमा प्रर्ोग भएको Node.js Runtime को version जाुँच गरी धनम्न version मा अपग्रडे गनहाु ोस। Current Version Required Action (Status) Node.js 26.x (Current LTS) Upgrade to 26.12.1 or later. Node.js 24.x (LTS) Upgrade to 24.22.1 or later. Node.js 22.x (LTS) Upgrade to 22.23.4 or later. Node.js 22.x reaches EOL on April 30, 2027. It is recommended to plan migration to Node.js 24 LTS or 26 LTS. Node.js 25.x, 23.x, 20.x, These End-of-Life versions do not receive the required 18.x or older (End-of-Life) security fixes. Upgrade to a supported, secure release line, preferably Node.js 24 LTS or 26 LTS, after compatibility testing.नेपाल सरकार प्रधानमन्त्री तथा मन्त्न्त्रपररषद्को कार्ाला र् सूचना प्रविधध तथा विद्यतु ीर् शासन कार्ाला र् राविर् साइबर सरु क्षा के न्त्र धसिंहदरबार, काठमाडौँ Advisory Number: NCSC-1146-115-05 धमधत: २०८३/०७/११ २. एकीकृ त डाटा व्र्िस्थापन के न्त्रमा होस्ट भएका प्रणालीहरुका सन्त्दभमा ा Runtime अद्यािधधक तथा सरु क्षा लर्ाच कार्ाान्त्िर्नका सम्बन्त्धमा थप प्राविधधक सहजीकरण आिश्र्क भएमा र्स के न्त्रका कम्लर्टु र अधधकृ त श्री आन्त्शष भट्ट (सम्पकाः ९८४४६८२७४२) तथा एकीकृ त डाटा व्र्िस्थापन के न्त्र (IDMC) का कम्लर्टु र अधधकृ त श्री मकु े श कुशिाहा (सम्पकाः 9861592301) सुँग आिश्र्क समन्त्िर् गनहाु नु अनरु ोध छ। ३. अद्यािधधक कार् ा सम्पन्न भएपधछ सम्बन्त्न्त्धत प्रणालीको सञ्चालन अिस्था तथा सरु क्षा परीक्षण गरी अद्यािधधक सफल भएको सधुनन्त्ित गनहाु ोस।् सरु क्षा कमजोरीको सम्भावित दरुु पर्ोग भएको आशङ्का भएमा सम्बन्त्न्त्धत प्रणालीका Log तथा अन्त्र् धडन्त्जटल प्रमाणहरू सरु न्त्क्षत रािी तत्काल र्स के न्त्रलाई जानकारी गराउनहु ोस।् Node.js अपग्रडे गने तररका Step 1: Check the currently installed version Run the following commands on each server or host running Node.js: node --version which -a node Step 2: Upgrade Node.js Upgrade to the latest patched release in the supported Node.js LTS. Use the official download page to obtain the appropriate installer or binary: https://nodejs.org/en/download For systems using Docker, update the base image to a patched Node.js image and rebuild the application image. If you use nvm, upgrade can be done with following commands: nvm install --ltsनेपाल सरकार प्रधानमन्त्री तथा मन्त्न्त्रपररषद्को कार्ाला र् सूचना प्रविधध तथा विद्यतु ीर् शासन कार्ाला र् राविर् साइबर सरु क्षा के न्त्र धसिंहदरबार, काठमाडौँ Advisory Number: NCSC-1146-115-05 धमधत: २०८३/०७/११ nvm use –lts Step 3: Rebuild and redeploy the application • Rebuild application artifacts, containers, and serverless functions using the patched runtime. • Redeploy the application and restart the affected services. • Ensure that no old or bundled Node.js binaries remain in use. Step 4: Verify the upgrade Run the following commands: node --version node -p "process.execPath" Confirm that the running application uses the patched Node.js runtime. Test application functionality and review logs for errors after deployment. Step 5: Apply additional security measures • Review applications that decompress Brotli-encoded requests or process responses from untrusted URLs. • Review DNS resolution, outbound request validation, and TLS certificate verification. • Check for signs of exploitation and preserve relevant logs. • If compromise is suspected, isolate the affected system as appropriate, notify the security team, and rotate potentially exposed credentials. Verify with npm audit or operating system package updates and confirm the patched version against the official Node.js security releases before deployment.
 Like
0
 Views
2
 Comments
0
 Share
0

Save

Report