


अत्यन्त जरुरी साइबर सुरक्षा एडभाइजरी
Summary
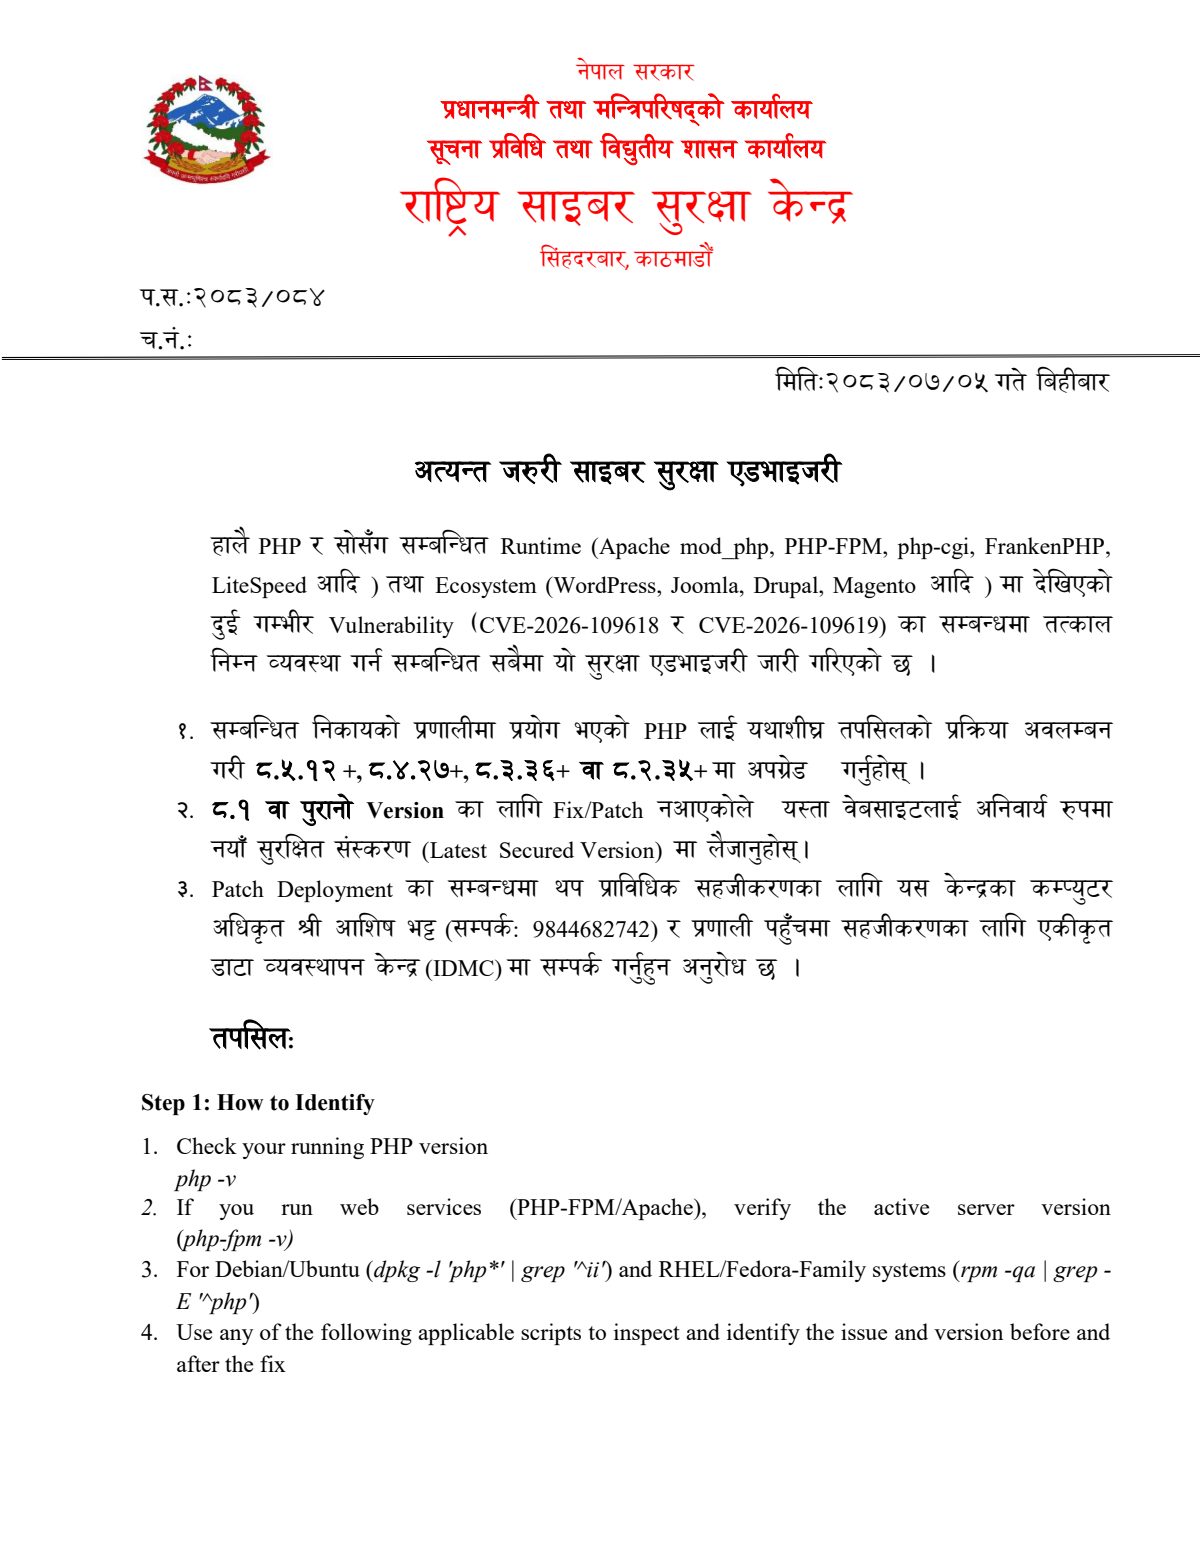
राष्ट्रिय साइबर सुरक्षा केन्द्र सिंहदरबार, काठमाडौँ Wa: अत्यन्त जरुरी साइबर सुरक्षा एडभाइजरी हालै PHP र सोसँग सम्बन्धित Runtime (Apache mod_php, PHP-FPM, php-cgi, FrankenPHP, LiteSpeed आदि ) तथा Ecosystem (WordPress, Joomla, Drupal, Magento आदि ) मा देखिएको दुई गम्भीर Vulnerability (CVE-2026-109618…
Auto-generated and may contain errors. Check the original notice before you act on it.
Files
- 00b74da1-bc9b-4ca8-9068-19dc6649e470.pdfPDF · 3 pages · 856 KBOpen
Key details
- Organization
- National Cyber Security Center Singhadurbar , Kathmandu
- Industry
- Gov. Authority/Autonomo. Body
- Category
- Others
- Published
- Notice date
- Fiscal year
- FY 2083/84
- Source
- View on the original website
Text extracted automatically from the notice (may contain errors)
नेपाल सरकार प्रधानमन्त्री तथा मन्त्रिपरिषद्को कार्यालय सूचना प्रबिधि तथा विद्युतीय शासन कार्यालय राष्ट्रिय साइबर सुरक्षा केन्द्र सिंहदरबार, काठमाडौँ प.स.:२०८३/०८४ Wa: fafa: 2053 08/04 गते बिहीबार अत्यन्त जरुरी साइबर सुरक्षा एडभाइजरी हालै PHP र सोसँग सम्बन्धित Runtime (Apache mod_php, PHP-FPM, php-cgi, FrankenPHP, LiteSpeed आदि ) तथा Ecosystem (WordPress, Joomla, Drupal, Magento आदि ) मा देखिएको दुई गम्भीर Vulnerability (CVE-2026-109618 र CVE-2026-109619) का सम्बन्धमा तत्काल निम्न व्यवस्था गर्न सम्बन्धित सबैमा यो सुरक्षा एडभाइजरी जारी गरिएको छ । १. सम्बन्धित निकायको प्रणालीमा प्रयोग भएको PHP लाई यथाशीघ्र तपसिलको प्रक्रिया अवलम्बन गरी ८.५.१२ 4+, ८.४.२७", ८.३.३६५ वा SBA अपग्रेड गर्नुहोस् | २. ८.१ बा पुरानो Version का लागि Fix/Patch नआएकोले यस्ता वेबसाइटलाई अनिवार्य रुपमा नयाँ सुरक्षित संस्करण (Latest Secured Version) मा लैजानुहोस्। 3. Patch Deployment का सम्बन्धमा थप प्राविधिक सहजीकरणका लागि यस केन्द्रका कम्प्युटर अधिकृत श्री आशिष भट्ट (सम्पर्क: 9844682742) र प्रणाली पहुँचमा सहजीकरणका लागि एकीकृत डाटा व्यवस्थापन केन्द्र (IDMC) मा सम्पर्क गर्नुहुन अनुरोध छ | 'तपसिलः Step 1: How to Identify 1. 2. Check your running PHP version php -v If you run web_ services (PHP-FPM/Apache), verify the active server version (php-fpm -v) For Debian/Ubuntu (dpkg -/ ‘php*' | grep 'Ni') and RHEL/Fedora-Family systems (7pm -qa | grep - E php’) Use any of the following applicable scripts to inspect and identify the issue and version before and after the fix नेपाल सरकार प्रधानमन्त्री तथा मन्त्रिपरिषद्को कार्यालय सूचना प्रबिधि तथा विद्युतीय शासन कार्यालय राष्ट्रिय साइबर सुरक्षा केन्द्र सिंहदरबार, काठमाडौँ प.स.:२०८३%०८४ Wa: https://github.com/NCSC-NL/php2shell https://github.com/Oxrsydn/php2shell-scan (A lightweight Python Utility) https://github.com/nukleer/CVE-2026-109618-109619-checker https://github.com/sxyrxyy/php2shell-cve-2026-109618-check https://github.com/corelight/php2shell-detect (Detection rules ) Step 2: How to Patch & Fix Upgrade your environment to the official patched versions immediately: ० PHP 8.5: Upgrade to 8.5.12 or later ० PHP 8.4: Upgrade to 8.4.27 or later ० PHP 8.3: Upgrade to 8.3.36 or later ० PHP 8.2: Upgrade to 8.2.35 or later System Commands for upgrade: ० Ubuntu/Debian: sudo apt update &&sudo apt upgrade php ७० RHEL/Rocky/CentOS: sudodnf update php ० Docker Users: Update your base images (e.g., php:8.3-fpm-alpine) and rebuild container images. Restart everything. Patching the binary on disk does nothing for running processes. Restart PHP-FPM, Apache, and every long-running PHP worker (queue workers, schedulers, daemons) so the patched binary is loaded. Validate Review the official advisories for both vulnerabilities and confirm whether your exact PHP build contains the fixes. https://www.php.net/archive/2026.php CVE-2026-109618: https://github.com/php/php-sre/security/advisories/GHSA-w8hw-w9fx-j79w CVE-2026-109619: https://github.com/php/php-sre/security/advisories/GHSA-6wmf-4rv5-p3rp नेपाल सरकार प्रधानमन्त्री तथा मन्त्रिपरिषद्को कार्यालय सूचना प्रबिधि तथा विद्युतीय शासन कार्यालय राष्ट्रिय साइबर सुरक्षा केन्द्र सिंहदरबार, काठमाडौँ प.स.:२०८३%०८४ च.नं.: Step 3: Full-Service Isolation (If Patching or Mitigations Must Wait) When to Use: Prioritise internet-facing systems. If a verified fix cannot be applied promptly, restrict public access or isolate the affected service. WAF and firewall rules may provide additional risk reduction, but the PHP project states that there are no complete mitigations: updating is the only safe choice. ० Restrict Network Access: Take exposed PHP applications off the public web. Enforce access strictly through an internal VPN, explicit IP allowlist, or Zero-Trust gateway ० Isolate EOL & High-Risk Stacks: If you run end-of-life PHP versions (8.1 or older) that receive no upstream security releases, place them into isolated network sandboxes and block egress traffic to stop lateral movement. ० Stop Vulnerable Services: If an internet-facing service cannot be patched or shielded, temporarily halt the runtime processing daemon: - PHP-FPM: sudosystemctl stop php*-fpm - Apache: sudosystemctl stop apache2 (or httpd) Windows: Stop the respective Windows Services via services.msc or PowerShell (Stop- Service w3svc, Stop-Service apache2.4). - Docker / Cloud Run: Scale deployments down to 0 replicas (docker stop <container> or kubectl scale deployment <app> --replicas=0).
 Like
0
 Views
2
 Comments
0
 Share
0

Save

Report